Selected work
A study of where the HTML shipped by an MCP App runs inside Claude.ai and what it can reach, with a probe app anyone can run again.
- Role
- Author
- Type
- Security writing
- Finding
- No vulnerability found
- Includes
- Runnable probe app
Signal path
- Input
- Hidden 01
- Hidden 02
- Output
The question
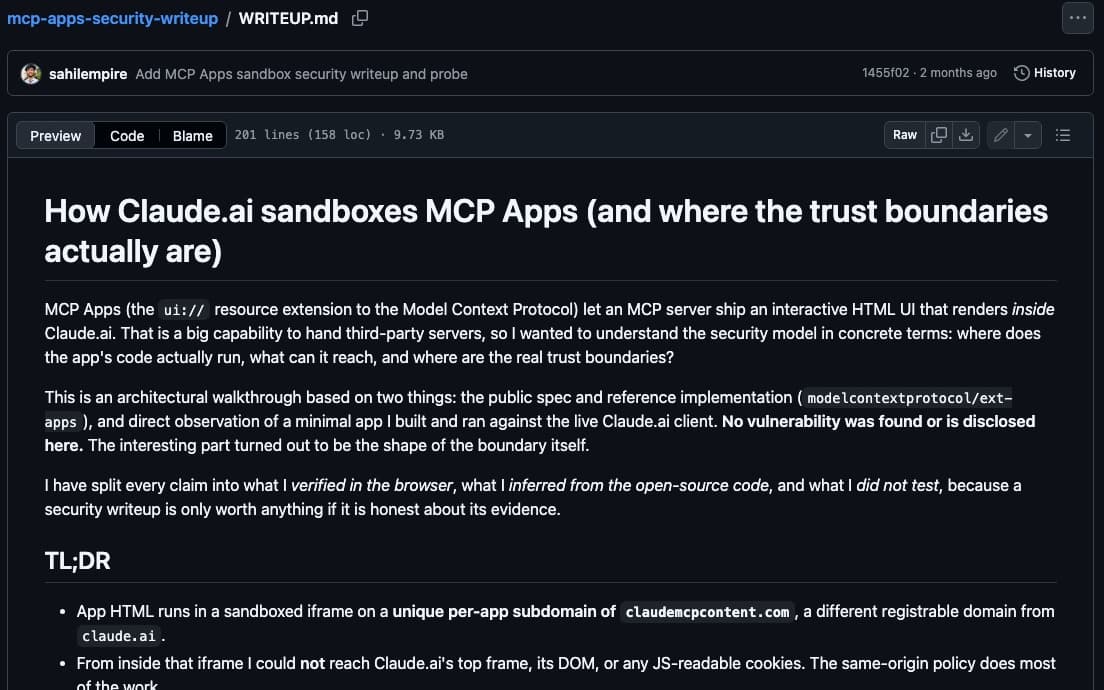
MCP Apps let a server ship an HTML interface that renders inside the host conversation. Before trusting that, I wanted to know where the HTML actually runs inside Claude.ai, what surrounds it, and what it is able to reach.
What I built
A small probe app and a written walkthrough of what it observed. The probe is an Express server built on the MCP SDK and the MCP Apps extension package, exposing one tool and one HTML resource. It is in the repository, so the observations can be repeated.
Where it stands
The writeup states plainly that no vulnerability was found. It is a map of the trust boundaries, not an exploit report, and it is public on GitHub together with the probe.
Method
- Input
Question
Where does the HTML of an MCP App run inside Claude.ai, and what can it reach?
Leads to: Probe app.
- Process
Probe app
An Express server exposing one tool and one HTML resource.
Leads to: Label.
- Decision
Label
Each finding is labelled by its evidence.
Leads to: Verified, Inferred, Not tested.
Verified
In the browser.
Leads to: Negative result.
Inferred
From the open source reference implementation.
Leads to: Negative result.
Not tested
Three questions were not tested.
Leads to: Open questions.
- Output
Negative result
No vulnerability found, and reported as that: a map of the trust boundaries.
Leads to: On GitHub.
- Store
Open questions
Listed in their own section, not folded into the conclusions.
Leads to: On GitHub.
- Output
On GitHub
The writeup together with the probe, so the observations can be repeated.
Approach
Every claim carries its evidence
Findings are labelled as verified in the browser, inferred from the open source reference implementation, or not tested. A reader can tell at a glance how much weight a sentence will bear.
A negative result, reported as one
Finding nothing is still a result. Writing it down saves the next person the same work, and keeps the conclusion from sounding bigger than it is.
Open questions left open
Three questions were not tested. They are listed in their own section as open questions, not folded into the conclusions.
Stack
- Model Context Protocol
- MCP Apps
- Express
- JavaScript